

About this conference
What to expect.
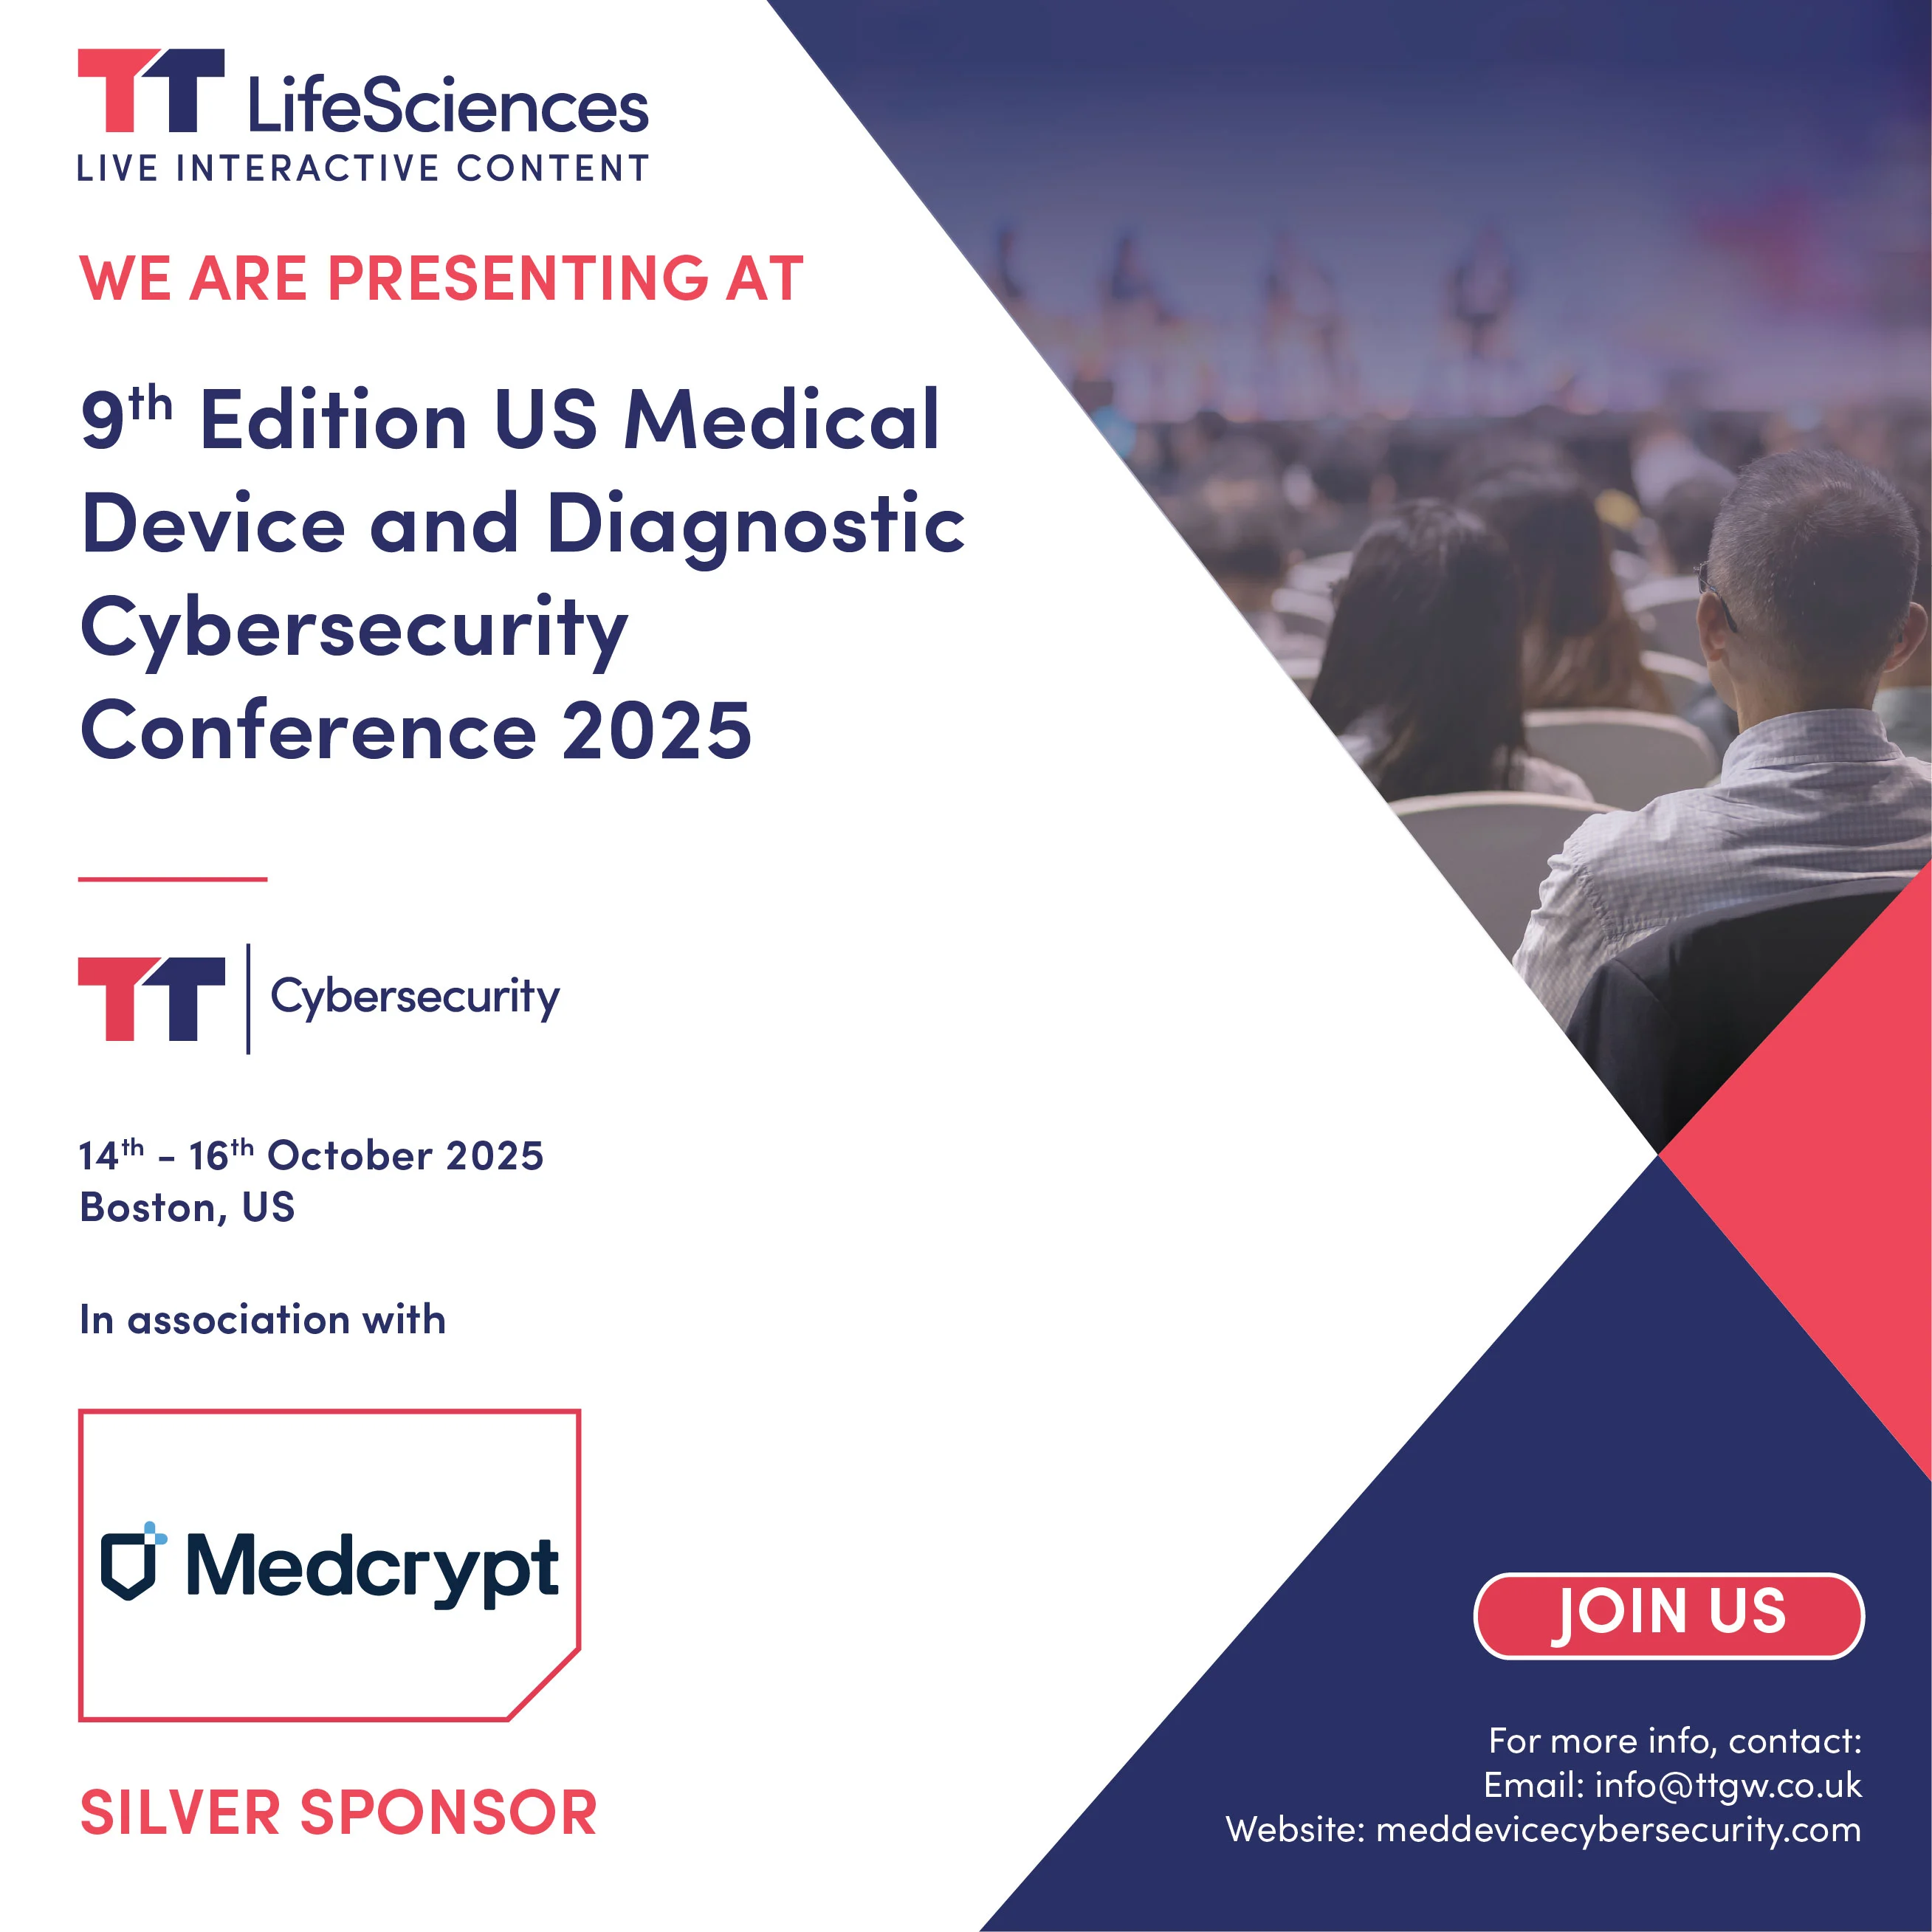
Medcrypt is proud to be a Silver Sponsor and featured presenter at the 9th Edition US Medical Device and Diagnostic Cybersecurity Conference, taking place October 14–16, 2025 in Boston, MA.
This year, we’re going beyond compliance checklists to help device manufacturers build scalable, secure-by-design programs that support both innovation and FDA expectations.
Join us for the following sessions: 1) Keynote: "Building & Maintaining a Regulatory-Ready SBOM: Best Practices Across the Lifecycle" Discover how leading manufacturers are building SBOM processes that withstand regulatory scrutiny and improve device security—without slowing development.
Takeaways:
- Evolving FDA and global expectations for SBOMs
- Lifecycle-aligned practices for SBOM accuracy and traceability
- How to get ahead of submission blockers
2) Workshop: "SBOM in Practice: Building, Automating & Operationalizing for FDA Compliance" A hands-on session covering tools, automation workflows, and continuous SBOM management practices for pre- and postmarket environments.
Takeaways:
- How to embed SBOM into DevOps and CI/CD
- Automation tips to reduce manual effort
- Using SBOMs to power real-time security monitoring
3) Roundtable: "Sharing Lessons Learned: Common Cybersecurity Pitfalls & How to Avoid Them" We’ll break down the most common issues manufacturers face, including:
- Security gaps due to missing documentation or supply chain oversight
- Incomplete threat modeling and pen testing programs
- Regulatory rejections tied to insufficient evidence of security maturity
- Postmarket gaps in vulnerability and incident management
This is the conference where real-world security meets regulatory reality. Medcrypt is here to help you bridge the gap.

