Case study · Plan & Benchmark Product Security
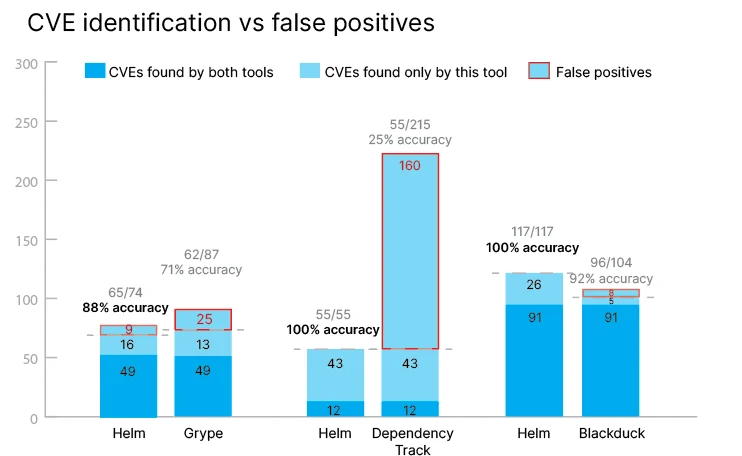
Helm Competitive Analysis: Outperforming Grype, Dependency Track, and Blackduck
How Helm achieves 96% accuracy while eliminating false positives that waste security teams' time
Read case study
Executive summary
Since the FDA’s 2016 Postmarket Cybersecurity Guidance, the rate of ICS-CERT medical device advisories has grown 386%, signaling stronger transparency but also persistent cybersecurity weaknesses.
This 2025 update expands Medcrypt’s decade-long analysis of 2013–2024 ICS-CERT medical device advisories, revealing that while industry maturity has improved, vulnerability trends remain remarkably consistent.
Key findings:
These data reveal that cybersecurity progress has plateaued — and that proactive risk management, not reactive disclosure, must define the next era of medical device security.
Why it matters
Even after eight years of formal postmarket expectations, many manufacturers continue to treat vulnerability management as reactive.
The FDA’s Section 524B now mandates timely updates and patching, but patch reference rates fell sharply in 2024.
This suggests that while manufacturers are more transparent, they remain resource-limited, compliance-driven, and dependent on legacy processes.
For regulators, manufacturers, and healthcare delivery organizations alike, these findings underscore an urgent need for:
Key insights
Go deeper on the topics in this whitepaper with Medcrypt analysis and real device programs.
Case study · Plan & Benchmark Product Security
How Helm achieves 96% accuracy while eliminating false positives that waste security teams' time
Read case study
Blog · Tools & Processes
Introduction Helm, developed by Medcrypt, emerges as a robust and precise SBOM (Software Bill of Materials) and Vulnerability Management Tool tailored to identify potential…
Read article
Case study · FDA Cybersecurity Readiness
From Manual Bottleneck to Automated Intelligence
Read case study