About this webinar
What to expect.
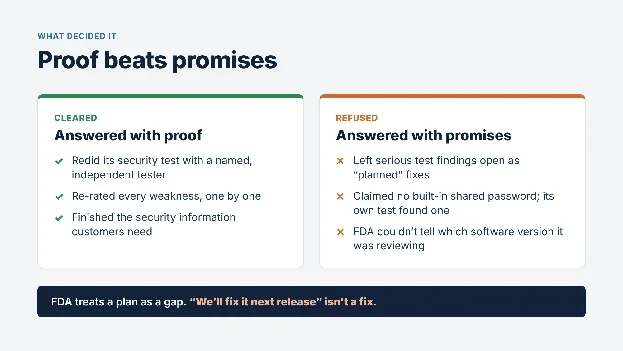
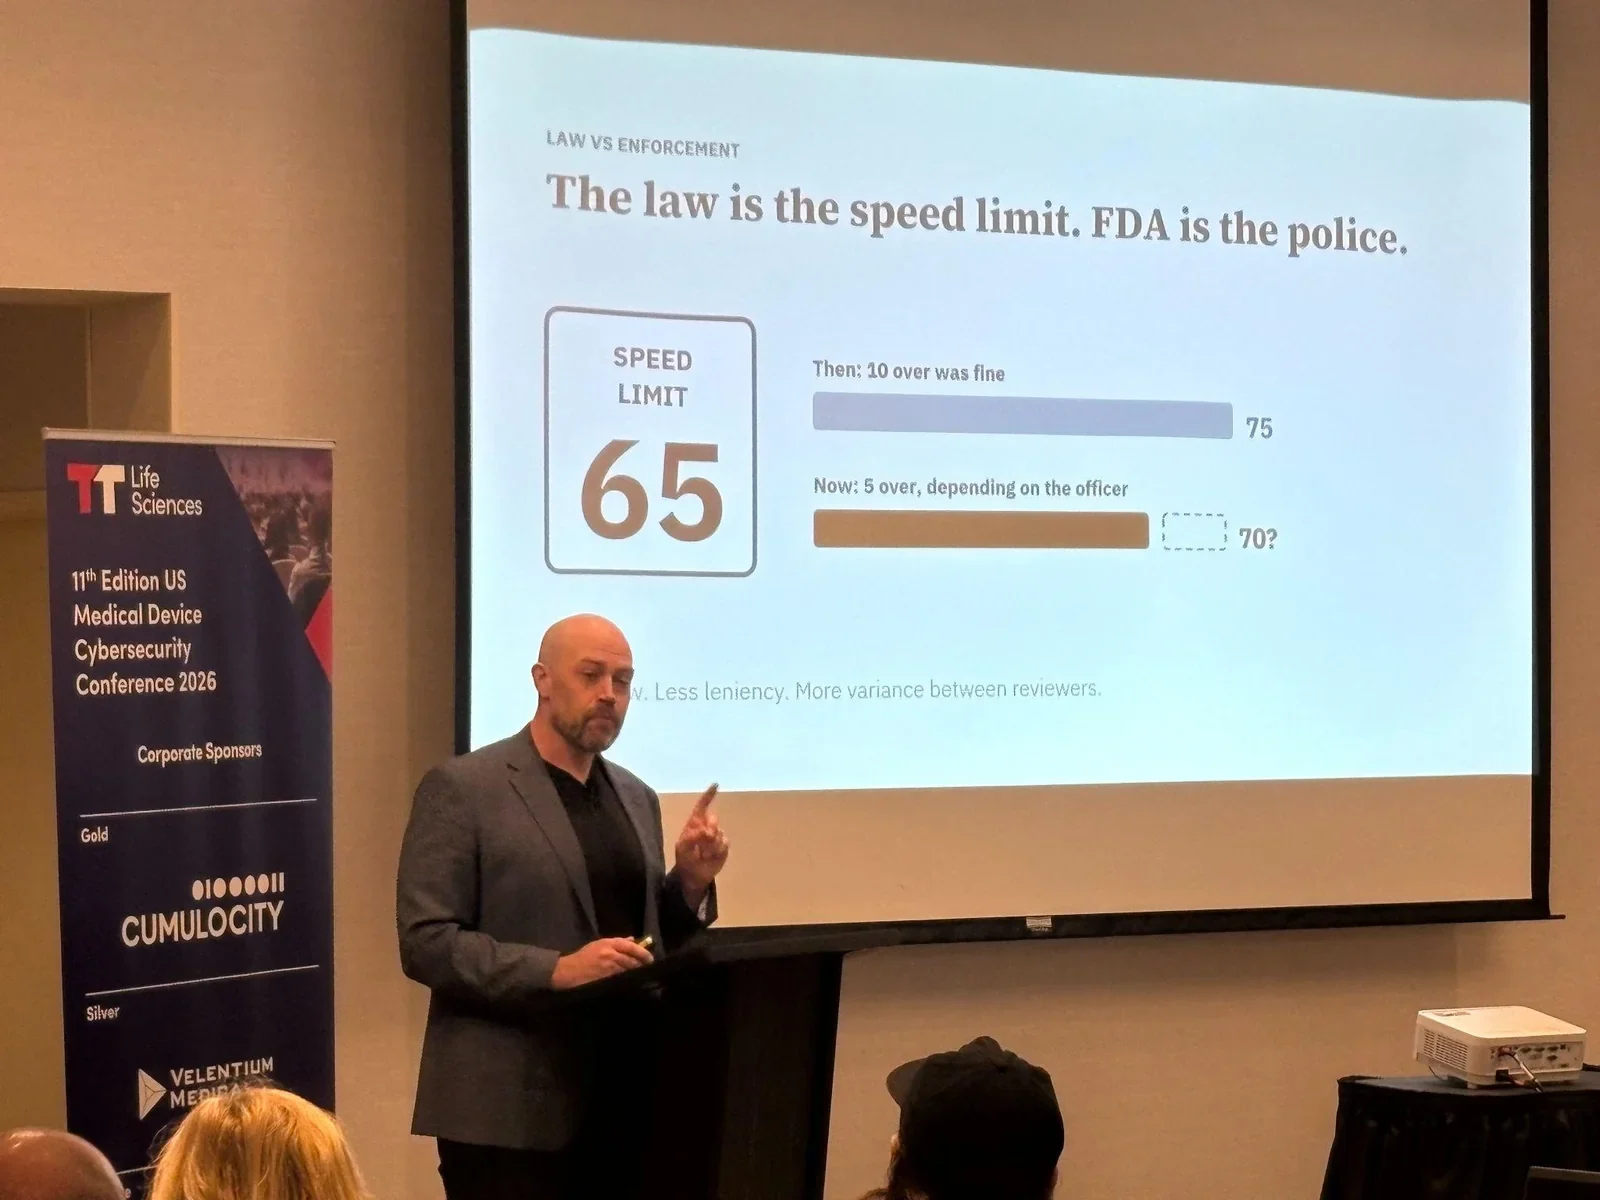
Cybersecurity has gone from a footnote to nearly half of FDA's deficiencies. Yet many teams are still debating how to score vulnerabilities instead of proving they've controlled them. Medcrypt's Seth Carmody and Axel Wirth walk through the current enforcement landscape, where CVSS helps and where it leaves you exposed, and what separated cleared submissions from refused ones in recent anonymized 510(k) reviews.
You'll learn:
- Why implementation evidence, not program design, separated cleared devices from refused ones
- How to use CVSS exploitability without treating the total score as risk
- Five pre-filing checks tied to real refusal grounds
- How one universal risk register connects vulnerability scores to the patient-harm decisions FDA expects